Token Settings
Numerous settings apply to tokens:
Per-user Settings
Single Factor Flag
When set (green checkmark in the Single Factor Flag column), the user can log in without a second factor. This setting is most useful in conjunction with the Auto Provisioning and Gradual Deployment settings described below.
Temporary Token
Selecting a user and clicking "Temporary Token Settings" will bring you to a page where you can add a temporary token to a user. You must specify an expiration date and the maximum number of logins for the temporary token.
Users with valid temporary tokens will have a green checkmark in the Temporary Token column.
Per-domain Settings
Domain configuration can be found under the "Configuration" tab in each GreenRADIUS domain.
Auto Provisioning
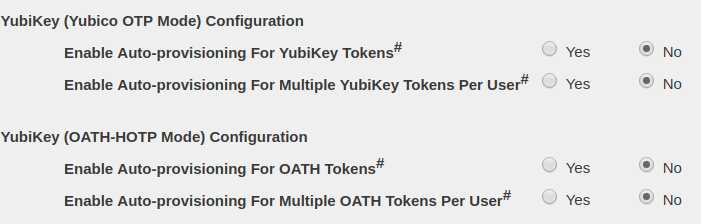
When Auto Provisioning is enabled, the first time a user logs in with a YubiKey OTP, that YubiKey will be automatically assigned to the user. The token assignment will appear on the Users/Groups tab.
The "Enable Auto Provisioning for Multiple Tokens Per User" options allow users to provision multiple tokens to themselves by this method. By default, only users with no tokens already assigned can auto provision.
The per-domain Auto Provisioning setting has no effect if it is not also enabled at a global level in the Global Configuration→General tab. (See below.)
Gradual Deployment
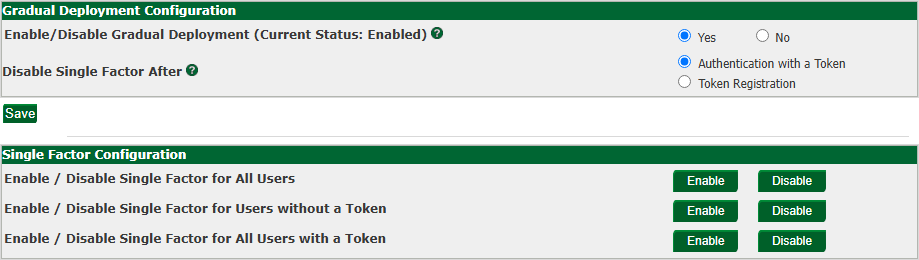 Gradual Deployment allows two-factor authentication to be enforced gradually as each user starts to use his or her token.
When Gradual Deployment is enabled, all users in the domain who have Single Factor enabled will be allowed to sign in with Single Factor (password-only). However, once a token is registered to the user or the user successfully uses their token for the first time (based on the 'Disable Single Factor After' setting), Single Factor will be disabled for that user, and they must use the token from that point forward, thus enforcing two-factor authentication.
When disabled, a user's Single Factor (password-only) status will remain unchanged after token registration or successful authentication with a token.
Note: This Gradual Deployment feature is not available for Windows Logon.
Single Factor Configuration
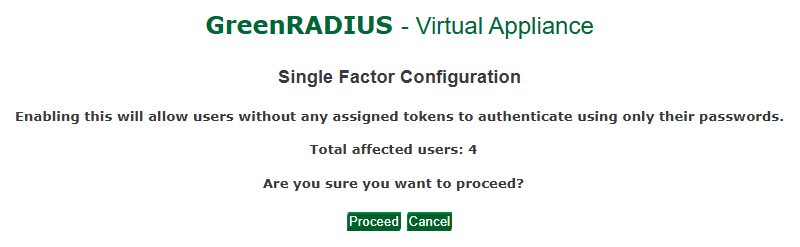
- Manage whether users can log in using single-factor authentication (bypassing two-factor authentication) or if a second factor is required.
- Enabled: Bypasses 2FA. Users ccan log in using single-factor authentication only.
- Disabled: Enforces 2FA. Users must provide a second factor to log in.
- Select which user group you want this configuration to apply to:
- All Users: Applies the policy across the entire domain.
- Users without a Token: Sets access for users without an assigned token (displays the count of affected users).
- All Users with a Token: Sets access for users with an active token (displays the count of affected users).
Note: You will be prompted for confirmation before applying any of these configuration changes.
Token Label Prefix

The Token Label Prefix is a text string which appears in Google Authenticator and other similar soft token apps to signify which Authenticator token is for GreenRADIUS integrated logins. This text string is configurable, but must not contain spaces.
Global Configuration
Token-related global configuration settings are found under the Global Configuration tab→General heading.
OTP Input Method

This setting controls where users input the OTP during login attempts. It is described in more detail in the Authentication Requests section.
Enable Auto Provisioning
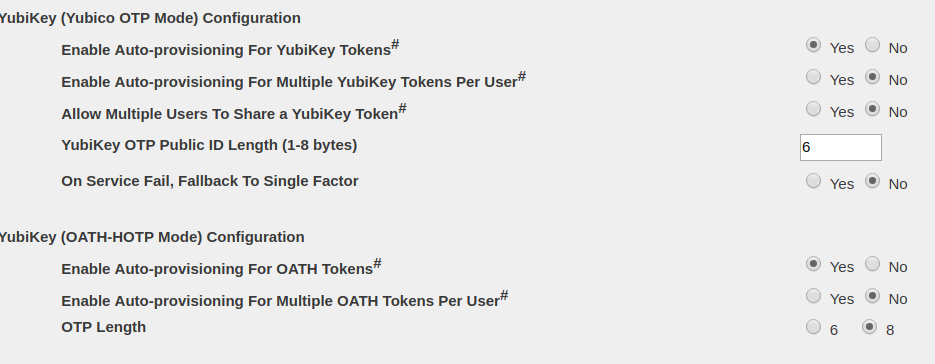
The Global Auto Provisioning settings must be enabled for any of the domain settings to have an effect. If Auto Provisioning is disabled in Global Configuration, no domain will have auto provisioning, irrespective of their domain settings.
© 2026 Green Rocket Security Inc. All rights reserved.